
About
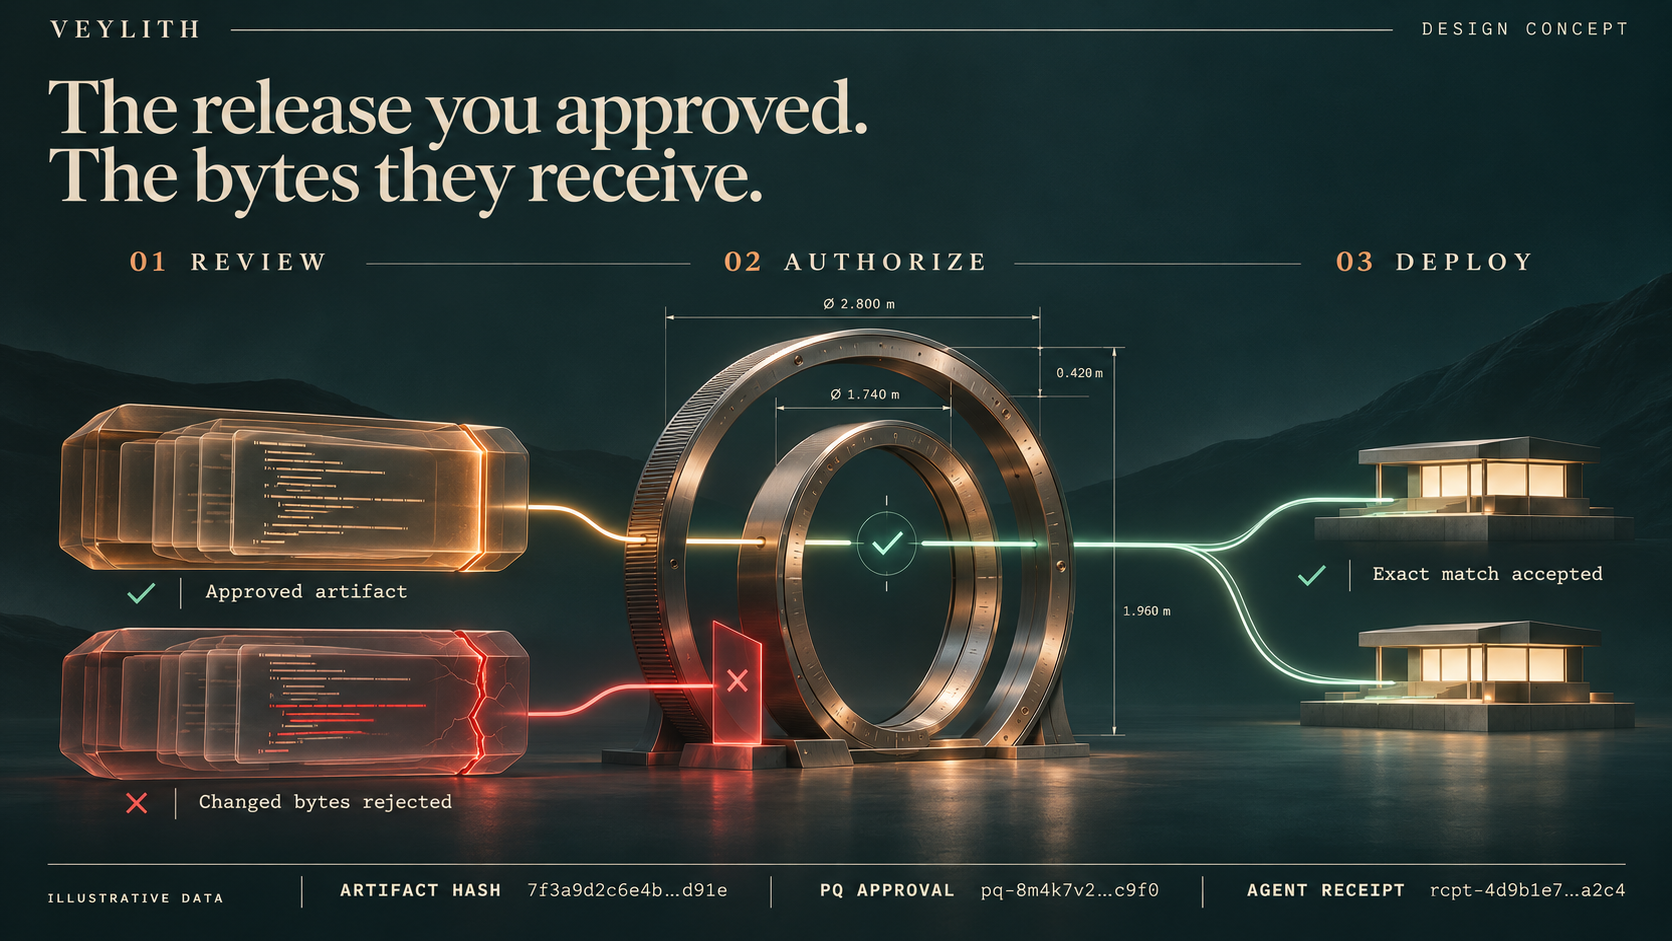
A compromised publishing key can replace a software download after reviewers approve it. Veylith makes deployment permission specific to the exact release. Two reviewers authorize an artifact and its manifest using post-quantum signatures. A controller on QoreChain verifies their approvals. Independent deployment agents check the downloaded bytes, target environment and current authorization before applying the release. Our working prototype demonstrates two local applications receiving an approved configuration, then rejecting substituted bytes, replayed approvals and a revoked release. The visual workbench makes every authorization, deployment and refusal inspectable. Veylith protects the approval-to-deployment boundary. It does not claim that approved software is inherently safe.
How it's made
Veylith combines a Solidity ReleaseController on qorechain-diana, QoreChain SDK 0.14.0, QoreSign 0.2.0, viem, two independent Node.js deployment-agent processes, and a React/Vite visual workbench. The controller requires two distinct registered ML-DSA-87 reviewer keys with proof of possession. It checks signatures through pqcVerify and key integrity through pqcKeyStatus. Approvals bind the chain, controller, project, environment, artifact hash, manifest hash, sequence, expiry and policy epoch. Policy rotation requires the existing quorum and invalidates the previous release. Hybrid native transactions open bounded, target-scoped EVM windows for release operations and explicitly close them afterward. Each agent fetches the actual HTTP-hosted manifest and configuration, verifies their fingerprints and current chain authorization, rechecks before application, and persists sequence protection. The demo applies bounded JSON configuration rather than executing downloaded code. Validation includes 13 passing Hardhat contract tests, 10 passing agent tests and nine passing live walkthrough checks. Public transaction evidence is included in the repository. Local contract tests use precompile mocks; the live walkthrough exercises the real Diana precompiles. Current reviewers are local demo identities. Browser-wallet signing, authenticated encrypted review packets and the required two-stage QCAI audit remain unfinished.
Timeline
New project.
Comments and questions
- No comments yet.