
Pushed 1 commit to main
- b7461c5 chore(pages): set Vite base /LatticeWard-protocol/, 404.html fallback, and ignore *.lwkey.json · Chinonso
Post-Quantum AI Agents
Post-Quantum Spend-Governance & Q-Day Immunity Engine for Autonomous AI Agents on QoreChain.
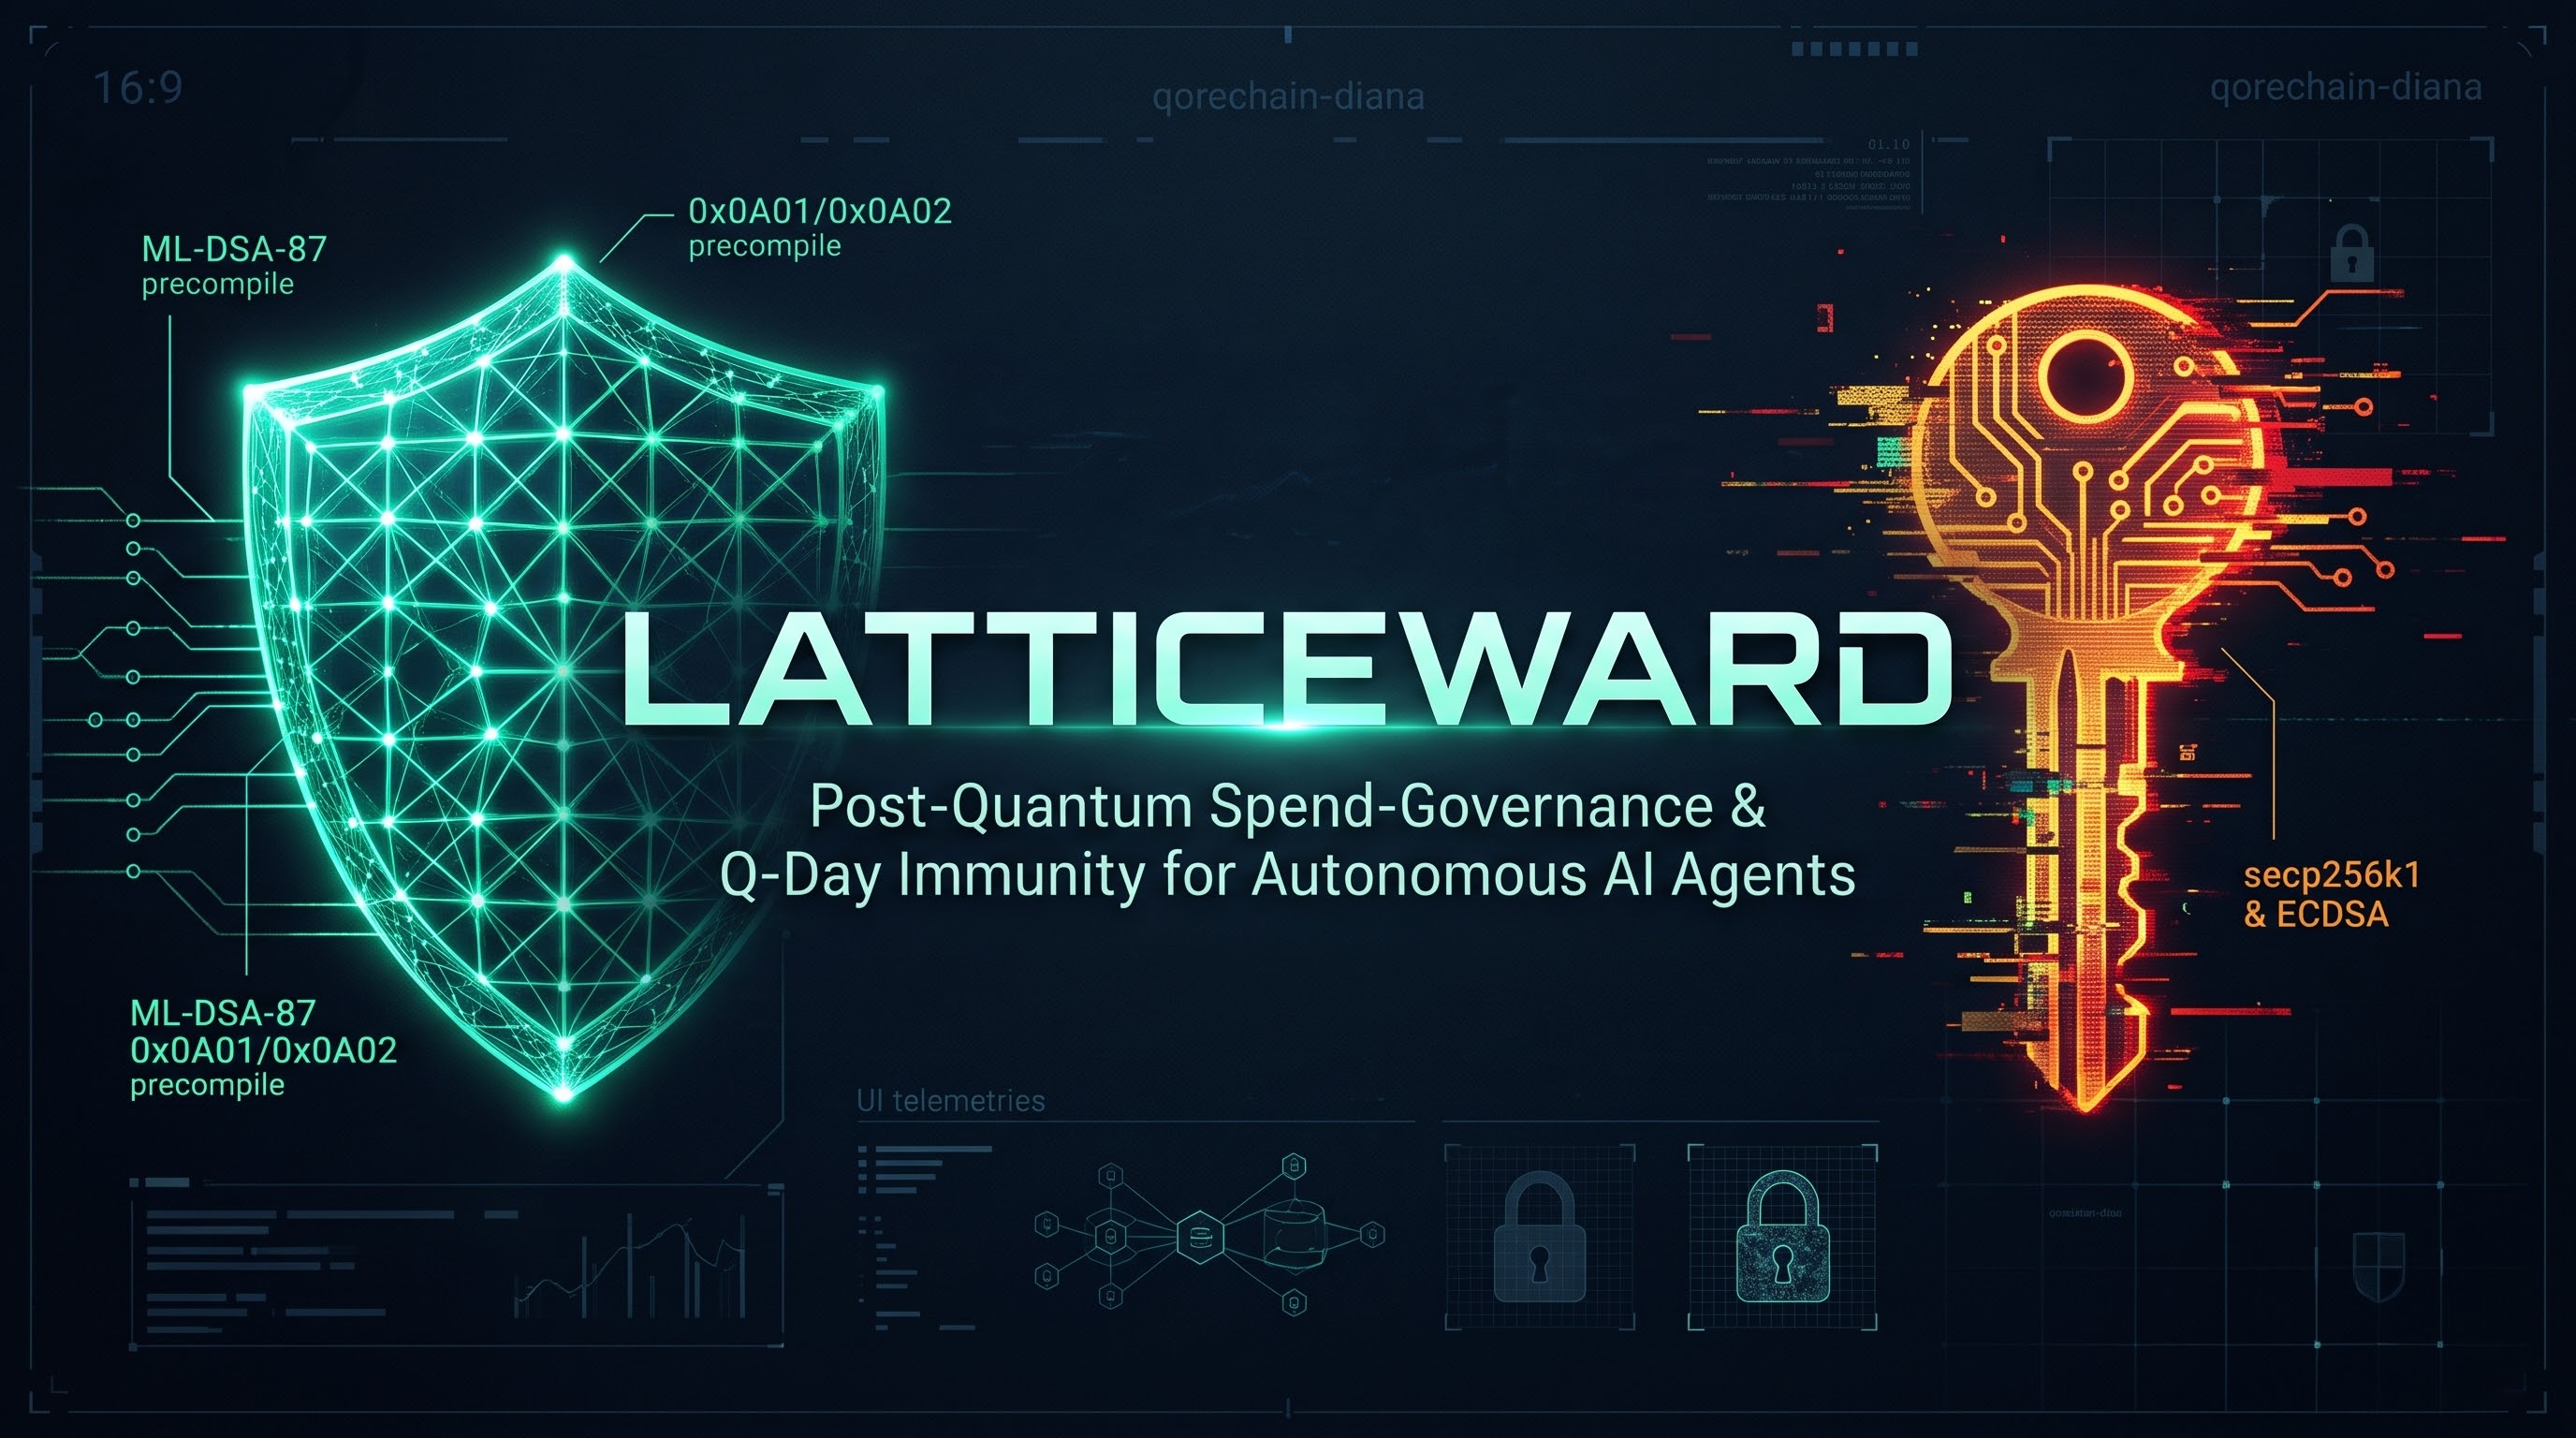
THE PROBLEM: HOT AGENT KEYS MEET Q-DAY Autonomous AI agents that run treasury tasks (payouts, recurring settlements) need a hot classical secp256k1 key to sign without a human popup. Today, a prompt injection or a server breach can leak that key. On Q-Day, Shor's algorithm will derive classical keys directly from public keys on-chain. A vault that relies on ecrecover for admin control loses everything. THE SOLUTION: LATTICEWARD LatticeWard is a treasury vault on qorechain-diana (chain ID 9800) that assumes every classical key will leak, and splits authority into two planes: 1. Execution plane (disposable classical key). The agent key can only pay out inside limits enforced on-chain: a maximum per payment, a rolling daily spend cap, a window expiry, an asset allowlist, replay-protected intents, and a recipient firewall. The firewall calls pqcKeyStatus (0x0A02) and refuses any recipient without a registered ML-DSA-87 key. 2. Sovereign plane (ML-DSA-87, FIPS 204). Every admin action (change policy, change limits, withdraw, rotate the agent key, emergency freeze and clawback through triggerQDayEmergencyClawback, rotate the sovereign key) needs a 4,627-byte ML-DSA-87 signature verified on-chain by pqcVerify (0x0A01). The signed message is bound to the chain ID, the vault address, a nonce and the exact parameters, so each signature works once. The contract has no ecrecover and no onlyOwner: msg.sender carries no admin authority, so a stolen classical key cannot administer the vault. 3. AI agent tooling. A fail-closed Zod schema lets the agent express only two things (execute within scope, or reject), so widening its own permissions cannot be written. A pre-flight step is wired to QoreChain's simulateWithRiskScore and fails closed: if the simulation is unavailable, nothing is sent. The public testnet endpoint does not serve it yet, so our live payouts rely on the vault's own on-chain checks. The vault is exposed through an MCP server with five tools, and a web page lets anyone check the live vault, test whether an address is quantum-safe, and run live attack simulations. PROOF: a live drill against the deployed vault passed all 8 checks on testnet: a valid payout, an over-spend blocked, a non-quantum-safe recipient blocked, a leaked-key policy hijack blocked, a leaked-key drain blocked, a replay blocked, then an ML-DSA-87 emergency clawback (key revoked, vault frozen) and recovery (unfrozen). The vault also holds 50 fUSD (ERC-20), converted from the faucet's bank coin with hybrid-signed ML-DSA-87 transactions. Transaction links are in the README. STATUS: testnet prototype, unaudited. Today one vault has one sovereign key, and admin signatures are made from a key file with our CLI. Per-user vaults and wallet-based signing are the next steps.
LatticeWard runs on the qorechain-diana testnet (EVM chain ID 9800). Vault: 0x9697a96058555b3A0C50b2338440C84B927caB29 (qor1j6t6jczc24dn5rzskgecgsxgfwf8e2efp7z6qp). 1. SMART CONTRACT (LatticeWardVault.sol) - Admin functions (configurePolicy, setAssetLimit, sovereignWithdraw, triggerQDayEmergencyClawback, emergencyClawback, rotateSovereignKey) call the ML-DSA-87 precompile at 0x0A01 through a fail-closed staticcall wrapper (QorePQC). Any precompile error, short return, or wrong key or signature length counts as "not verified". The digest is keccak256 of the domain, chain ID, vault address, policy nonce, action tag and the hash of the exact parameters. The nonce moves on every successful admin action, so signatures cannot be replayed. - executeScopedAgentIntent enforces per-asset limits, a rolling epoch cap, the window expiry, an asset allowlist, intent-ID replay protection and the 0x0A02 recipient check. State changes before the transfer, and OpenZeppelin's ReentrancyGuard covers every function that moves funds. - Hardening: bounded epoch duration, sane limit checks, and no way to pay the vault to itself. - Found along the way: the 0x0A01 precompile takes its arguments in the order (public key, signature, message). We found this by probing the live chain, not from documentation. 2. TESTING - Foundry: 32 tests (unit, fuzz and invariant). The invariant tests simulate an attacker holding only classical keys who throws random calls and forged signatures at the vault and can never move funds or change admin state. - A live testnet drill script (npm run verify:qday) runs the 8 scenarios against the deployed vault and records the transactions. - QoreScan (@qorechain/qorescan) generated a crypto bill of materials for the Solidity sources. 3. AGENT RUNTIME AND MCP - A strict Zod schema (execute within scope or reject) means a prompt injection cannot express a policy change. - The pre-flight step is wired to simulateWithRiskScore from @qorechain/sdk. It is fail-closed, with no fallback in the code: if the simulation is unavailable, nothing is sent. - An MCP server (@modelcontextprotocol/sdk) exposes five latticeward tools: vault and PQC status, simulate intent, execute scoped settlement, run the drill, and verify a receipt. - Sovereign signing uses ML-DSA-87 from @noble/post-quantum, with the contract itself supplying the digest so there is a single source of truth. - A script converts faucet fUSD (bank coin) to ERC-20 with hybrid-signed MsgConvertCoin transactions through @qorechain/sdk. WHAT WAS HARD QoreChain admits an EVM transaction only from an account with a registered ML-DSA-87 key and an open authorisation window. That window bounds native QOR value but not token amounts, so we added the missing layer: the vault caps amounts and checks recipients inside the contract.
Pushed 1 commit to main
Pushed 1 commit to main
Pushed 1 commit to main
Pushed 1 commit to main
Pushed 1 commit to main
Newly verified on chain: QoreScan
Pushed 1 commit to main
Pushed 1 commit to main
Pushed 1 commit to main
Pushed 1 commit to main
Pushed 1 commit to main
Earned a Ship Weeks badge.
Newly verified on chain: EVM window (incl. scoped)
Pushed 1 commit to main
Newly verified on chain: QoreScan
Pushed 3 commits to main
Pushed 1 commit to main
Pushed 1 commit to main
Earned a Ship Weeks badge.